The Cyber Security Policy Template: What Your Policy Should Contain
Before you’ve even considered a cyber incident response plan or business impact analysis your business will need to outline a set of hard and fast cybersecurity rules. A good cybersecurity policy can range in size from a single page to a small book. But at the very least, the below principles that you can use to use as an outline for a cyber security policy template, should be addressed coupled with giving your employees a general talk on cybersecurity to stress its importance.
Password management
A password should be as hard to guess as possible. This means passwords should be changed regularly and be complex with a mixture of numbers and letters. Two-factor authentication is also a wise complement to well-managed passwords. And you should also prevent employees from using the same password on different sites.
Locking of devices
If an employee leaves their device unattended in say an airport or a coffee shop, an opportunist criminal can, in theory, access a breadth of sensitive data. However, if you instil in your employees the simple habit of locking devices when not in use, then this potentially serious threat is eliminated.
Social media privacy settings
This is as much a “life best practice” as it is part of a cybersecurity policy template. Telling your employees to apply maximum settings to social media accounts will limit the amount of information freely available online. It will help if an employee ever talks a little too freely about sensitive company matters. However, it will also help keep secret seemingly irrelevant data like employee names and birthdays. Data like this is valuable to email scammers looking to create insightful and targeted email attacks.
Regular patching and updating
Not all programs update themselves automatically. And out-of-date software can end up being the weak point criminals are looking for. Make sure you set your software to auto-update wherever possible and perform regular scans to check for any software that hasn’t been updated.
Compliance considerations
This will vary from industry to industry but there can be a range of security rules set by the government that all businesses within that industry will have to adhere to. This will often relate to the safeguarding of customer data – particularly common within industries like health and legal. Make sure you pay close attention to your compliance requirements as at the very least they can help you start writing your cybersecurity policy.
Cyber awareness training
One of the most important security principles and something every business should do. Since employees are the first and weakest line of defence, phishing scams are the most popular form of attack – not to mention the easiest to execute. Employees need to know how to spot all types of phishing scams a mile off and know just what to do when they appear.
Next Steps
A cybersecurity policy template like this should form a fundamental part of your small business security. Beyond that though, you’ll need to be protected in case your cybersecurity measures fail you. With a solid Business Continuity Disaster Recovery Plan, your business can have the ultimate response to any form of disaster. Cyber-attack or otherwise.
Click below to download our BCDR eBook today or contact us to discover how we can help you and your staff work more securely.
Featured post
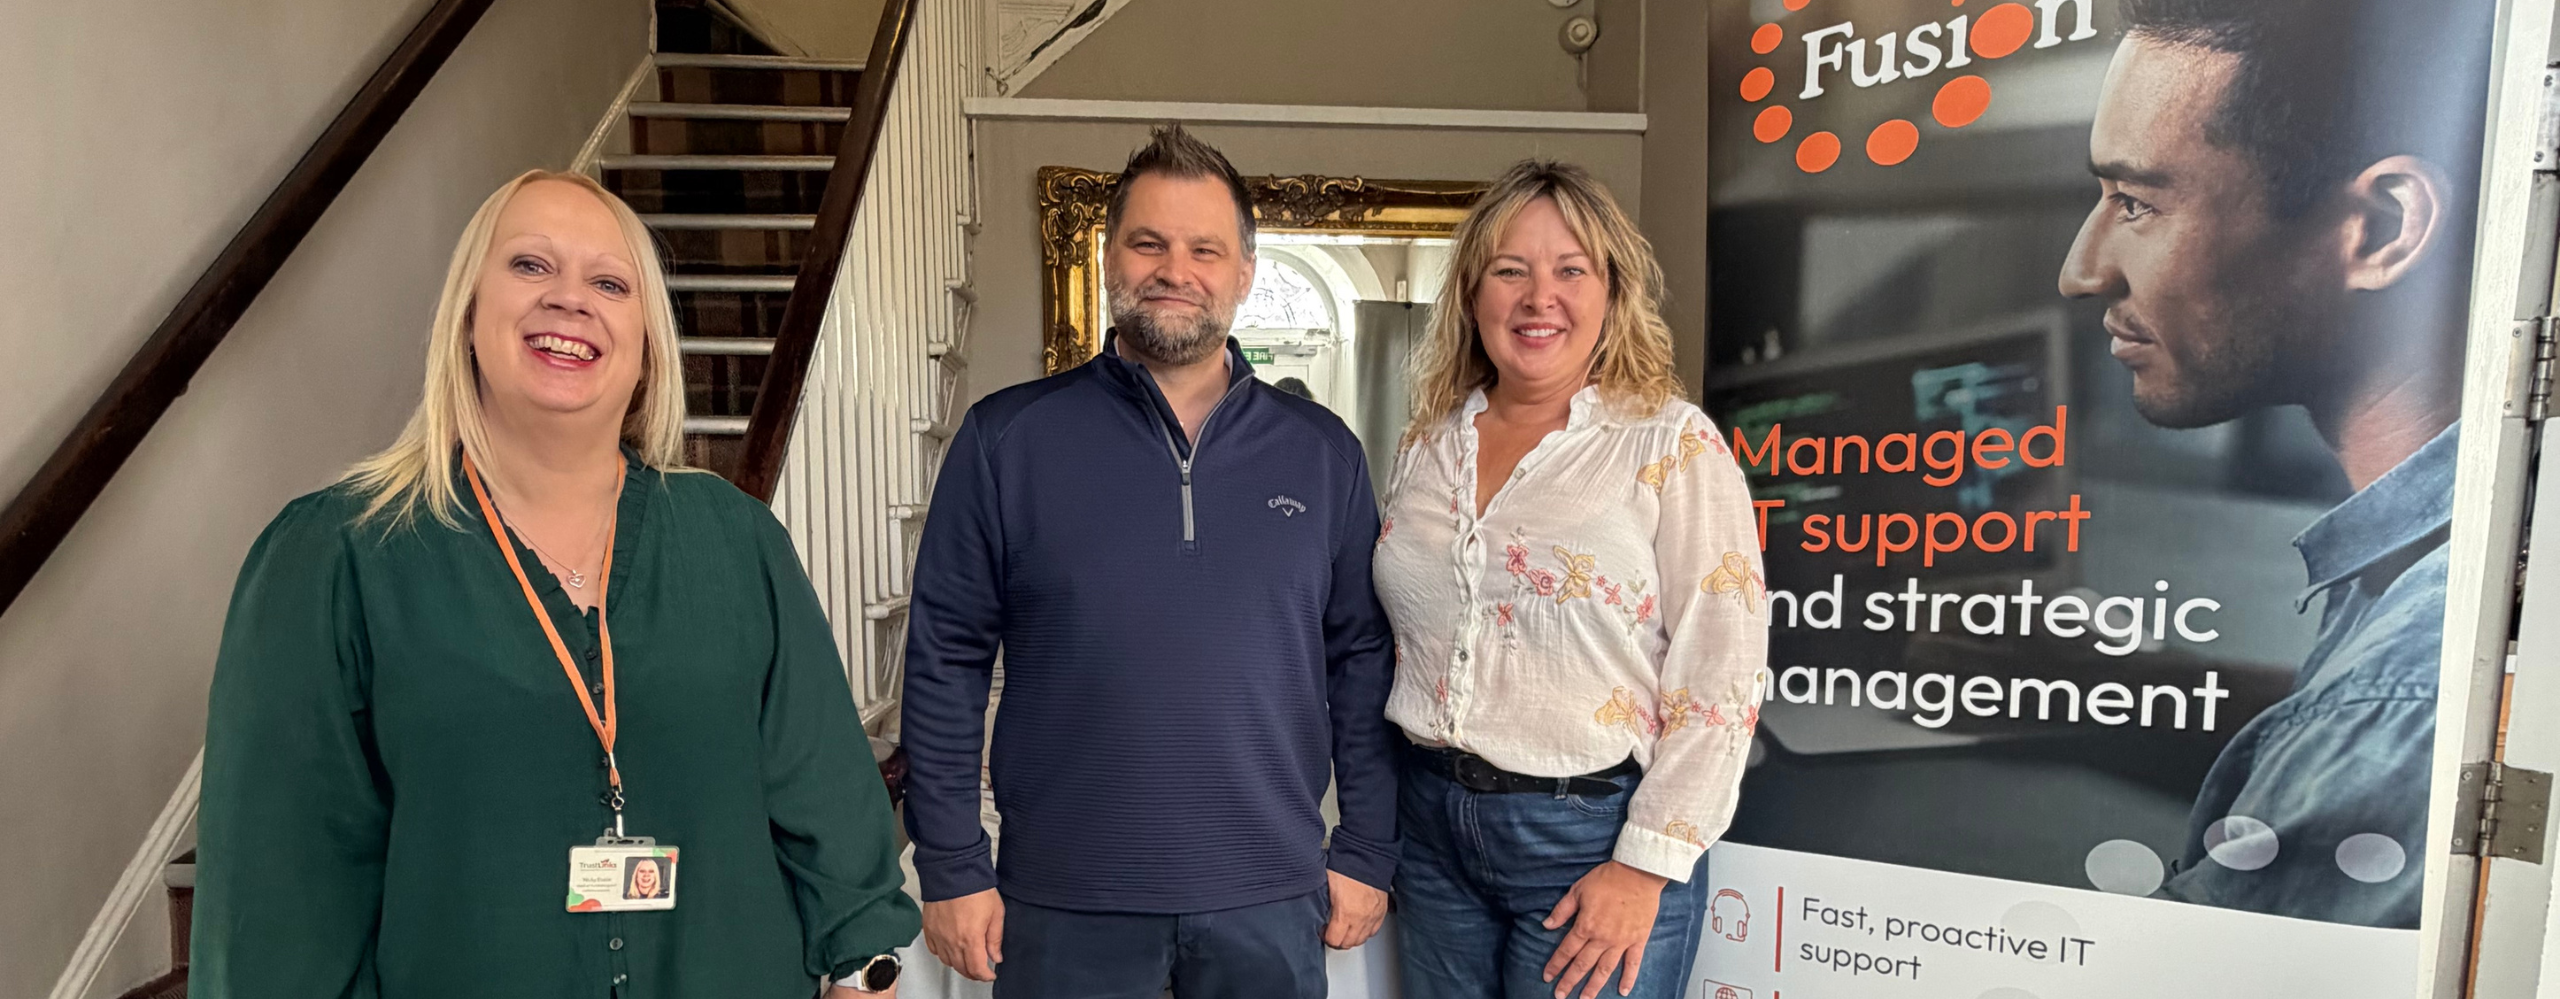
Fusion Supports TrustLinks at their 2026 Charity Golf Day
Fusion Technology Solutions was proud to be the headline sponsor of the TrustLinks 2026 Charity Golf Day this month, supporting an important local cause dedicated to improving mental health and wellbeing.
Recent posts
Latest posts
Fusion Supports TrustLinks at their 2026 Charity Golf Day
Fusion Technology Solutions was proud to be the headline sponsor of the TrustLinks 2026 Charity Golf Day this month, supporting an important local cause dedicated to improving mental health and wellbeing.
Common mistakes businesses make when switching to VoIP
With the UK's PSTN switch-off continuing to reshape the telecommunications landscape, more organisations are making the move to VoIP than ever before. However, while the benefits are significant, a poorly planned migration can lead to unnecessary disruption.
Case Study: Building Coriant a secure, reliable and scalable foundation for sustainable growth
Coriant is a dynamic and expanding force in industrial services, focused on the maintenance of assets across critical industries. With approximately 300 staff spread across seven office locations, the company has been on an exciting growth trajectory, including strategic acquisitions that have broadened their capabilities and market reach.